☑ Aggancia questa barra allo schermo | ☐ Disattiva gli effetti grafici
✖

Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.

Slackware Linux e risoluzione di problemi, di Andrea Peluso


ChangeLog repository

Repository Rss

blender-3.0.1-x86_64-1_ap.txz:  Upgraded.

ChangeLog Slackware current

ChangeLog x86 Rss - ChangeLog x86_64 Rss

a/libblockdev-3.6.0-x86_64-1.txz:  Upgraded.
a/usb_modeswitch-2.6.3-x86_64-1.txz:  Upgraded.
d/autoconf-archive-2026.11.11-noarch-1.txz:  Upgraded.
d/dkms-3.4.5-x86_64-1.txz:  Upgraded.
d/flex-2.6.9-x86_64-1.txz:  Upgraded.
d/git-2.56.1-x86_64-1.txz:  Upgraded.
  This update fixes security issues.
  For more information, see:
    https://gitlab.com/git-scm/git/-/blob/HEAD/Documentation/RelNotes/2.56.1.adoc
    https://gitlab.com/git-scm/git/-/blob/HEAD/Documentation/RelNotes/2.50.2.adoc
    https://www.cve.org/CVERecord?id=CVE-2026-111760
    https://www.cve.org/CVERecord?id=CVE-2026-113408
    https://www.cve.org/CVERecord?id=CVE-2026-114466
    https://www.cve.org/CVERecord?id=CVE-2026-114467
    https://www.cve.org/CVERecord?id=CVE-2026-114469
    https://www.cve.org/CVERecord?id=CVE-2026-105437
  (* Security fix *)
kde/digikam-9.1.0-x86_64-8.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
kde/kimageformats-6.31.0-x86_64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
kde/kimageformats5-5.116.0-x86_64-4.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
kde/krita-6.0.4.1-x86_64-3.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/appstream-1.2.3-x86_64-1.txz:  Upgraded.
l/avahi-0.9_rc5-x86_64-1.txz:  Upgraded.
l/ffmpeg-9.0.2-x86_64-3.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/imagemagick-7.1.2_35-x86_64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/libjxl-0.13.0-x86_64-1.txz:  Upgraded.
  Shared library .so-version bump.
l/libtatsu-1.1.1-x86_64-1.txz:  Upgraded.
l/libvips-8.18.7-x86_64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/qtkeychain-0.18.0-x86_64-1.txz:  Upgraded.
l/sip-6.17.3-x86_64-1.txz:  Upgraded.
n/autofs-5.2.0-x86_64-1.txz:  Upgraded.
n/httpd-2.4.71-x86_64-1.txz:  Upgraded.
  This update fixes bugs and security issues:
  Heap corruption and RCE in assign_headers.
  mod_vhost_alias 1 byte stack buffer overwrite.
  mod_md NULL pointer dereference leads to child process crash.
  For more information, see:
    https://downloads.apache.org/httpd/CHANGES_2.4.71
    https://www.cve.org/CVERecord?id=CVE-2026-119618
    https://www.cve.org/CVERecord?id=CVE-2026-109163
    https://www.cve.org/CVERecord?id=CVE-2026-106023
  (* Security fix *)
n/mobile-broadband-provider-info-20261111-noarch-1.txz:  Upgraded.
n/sshfs-3.7.7-x86_64-1.txz:  Upgraded.
x/ibus-table-1.19.0-x86_64-1.txz:  Upgraded.
x/mesa-26.2.7-x86_64-1.txz:  Upgraded.
xap/freerdp-3.33.1-x86_64-1.txz:  Upgraded.
  This update fixes security issues.
  For more information, see:
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-x863-43r4-f7c2
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-m33m-4qxh-hq76
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-52rf-pppx-qm55
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-3664-pr8r-3254
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-rp99-f9qv-c446
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-23fv-6wrf-5hfq
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-f6v9-vx5q-vjpf
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-m6hp-4798-x78x
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-9c9j-2r7q-5gx2
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-ch3p-5r9r-w86p
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-76c4-7552-ffhv
  (* Security fix *)
xap/geeqie-3.4-x86_64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
xap/gimp-3.2.8-x86_64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
extra/tigervnc/tigervnc-1.16.2-x86_64-8.txz:  Rebuilt.
  Recompiled against xorg-server-21.1.26 to fix these security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  XRes QueryClientIds Request Size Overflow.
  XRes QueryResourceBytes Swap Path Size Overflow.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109904
    https://www.cve.org/CVERecord?id=CVE-2026-109094
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
testing/packages/mesa-26.3.0-x86_64-1.txz:  Upgraded.

a/exfatprogs-1.4.4-x86_64-1.txz:  Upgraded.
a/intel-microcode-20261110-noarch-1.txz:  Upgraded.
a/kernel-firmware-20261109_69e51bb-noarch-1.txz:  Upgraded.
a/kernel-generic-7.3.4-x86_64-1.txz:  Upgraded.
a/kmscon-10.1.1-x86_64-2.txz:  Rebuilt.
  kmscon.conf: set dpms-timeout=3600 to blank the screen after an hour instead
  of the default ten minutes.
a/sysvinit-scripts-16.0-noarch-13.txz:  Rebuilt.
  rc.modules: support loading modules from modules-load.d/ files, such as the
  one shipped in the ddcutil package.
  Thanks to gcosbug and ZhaoLin1457.
d/automake-1.20-noarch-1.txz:  Upgraded.
d/flex-2.6.5-x86_64-1.txz:  Upgraded.
d/kernel-headers-7.3.4-x86-1.txz:  Upgraded.
k/kernel-source-7.3.4-noarch-1.txz:  Upgraded.
  -SATA_INIC162X y
   DRM m -> y
   NOVA_CORE n -> m
  +DRM_NOVA m
kde/stellarsolver-2.9-x86_64-1.txz:  Upgraded.
l/libgnt-2.15.0-x86_64-1.txz:  Upgraded.
l/libodfgen-0.1.9-x86_64-1.txz:  Upgraded.
l/libxmlb-0.3.30-x86_64-1.txz:  Upgraded.
l/lz4-1.11.1-x86_64-1.txz:  Upgraded.
x/xorg-server-21.1.26-x86_64-1.txz:  Upgraded.
  This update fixes security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  XRes QueryClientIds Request Size Overflow.
  XRes QueryResourceBytes Swap Path Size Overflow.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109904
    https://www.cve.org/CVERecord?id=CVE-2026-109094
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
x/xorg-server-xephyr-21.1.26-x86_64-1.txz:  Upgraded.
x/xorg-server-xnest-21.1.26-x86_64-1.txz:  Upgraded.
x/xorg-server-xvfb-21.1.26-x86_64-1.txz:  Upgraded.
x/xorg-server-xwayland-24.1.15-x86_64-1.txz:  Upgraded.
  This update fixes security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  XRes QueryClientIds Request Size Overflow.
  XRes QueryResourceBytes Swap Path Size Overflow.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109904
    https://www.cve.org/CVERecord?id=CVE-2026-109094
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
xap/mozilla-firefox-153.7.0esr-x86_64-1.txz:  Upgraded.
  This update contains security fixes and improvements.
  For more information, see:
    https://www.mozilla.org/en-US/firefox/153.7.0/releasenotes/
    https://www.mozilla.org/security/advisories/mfsa2026-127
    https://www.cve.org/CVERecord?id=CVE-2026-124853
    https://www.cve.org/CVERecord?id=CVE-2026-124854
    https://www.cve.org/CVERecord?id=CVE-2026-124855
    https://www.cve.org/CVERecord?id=CVE-2026-124856
    https://www.cve.org/CVERecord?id=CVE-2026-124857
    https://www.cve.org/CVERecord?id=CVE-2026-124858
    https://www.cve.org/CVERecord?id=CVE-2026-124859
    https://www.cve.org/CVERecord?id=CVE-2026-124860
    https://www.cve.org/CVERecord?id=CVE-2026-124861
    https://www.cve.org/CVERecord?id=CVE-2026-124862
    https://www.cve.org/CVERecord?id=CVE-2026-118007
    https://www.cve.org/CVERecord?id=CVE-2026-124863
    https://www.cve.org/CVERecord?id=CVE-2026-124864
    https://www.cve.org/CVERecord?id=CVE-2026-124865
    https://www.cve.org/CVERecord?id=CVE-2026-124866
    https://www.cve.org/CVERecord?id=CVE-2026-124868
    https://www.cve.org/CVERecord?id=CVE-2026-124869
    https://www.cve.org/CVERecord?id=CVE-2026-124870
    https://www.cve.org/CVERecord?id=CVE-2026-124872
    https://www.cve.org/CVERecord?id=CVE-2026-124873
    https://www.cve.org/CVERecord?id=CVE-2026-124874
    https://www.cve.org/CVERecord?id=CVE-2026-124875
    https://www.cve.org/CVERecord?id=CVE-2026-124876
    https://www.cve.org/CVERecord?id=CVE-2026-124877
    https://www.cve.org/CVERecord?id=CVE-2026-124879
    https://www.cve.org/CVERecord?id=CVE-2026-124880
    https://www.cve.org/CVERecord?id=CVE-2026-124881
    https://www.cve.org/CVERecord?id=CVE-2026-124882
    https://www.cve.org/CVERecord?id=CVE-2026-124883
    https://www.cve.org/CVERecord?id=CVE-2026-124884
    https://www.cve.org/CVERecord?id=CVE-2026-124885
    https://www.cve.org/CVERecord?id=CVE-2026-124886
    https://www.cve.org/CVERecord?id=CVE-2026-124887
    https://www.cve.org/CVERecord?id=CVE-2026-124888
    https://www.cve.org/CVERecord?id=CVE-2026-124889
    https://www.cve.org/CVERecord?id=CVE-2026-124890
    https://www.cve.org/CVERecord?id=CVE-2026-124891
    https://www.cve.org/CVERecord?id=CVE-2026-124892
    https://www.cve.org/CVERecord?id=CVE-2026-124893
    https://www.cve.org/CVERecord?id=CVE-2026-124894
    https://www.cve.org/CVERecord?id=CVE-2026-124895
    https://www.cve.org/CVERecord?id=CVE-2026-124896
    https://www.cve.org/CVERecord?id=CVE-2026-124897
    https://www.cve.org/CVERecord?id=CVE-2026-124898
    https://www.cve.org/CVERecord?id=CVE-2026-124899
    https://www.cve.org/CVERecord?id=CVE-2026-124901
    https://www.cve.org/CVERecord?id=CVE-2026-124902
    https://www.cve.org/CVERecord?id=CVE-2026-124903
    https://www.cve.org/CVERecord?id=CVE-2026-124905
    https://www.cve.org/CVERecord?id=CVE-2026-124906
    https://www.cve.org/CVERecord?id=CVE-2026-124907
    https://www.cve.org/CVERecord?id=CVE-2026-124909
    https://www.cve.org/CVERecord?id=CVE-2026-124910
    https://www.cve.org/CVERecord?id=CVE-2026-124912
    https://www.cve.org/CVERecord?id=CVE-2026-118019
    https://www.cve.org/CVERecord?id=CVE-2026-124913
    https://www.cve.org/CVERecord?id=CVE-2026-124914
    https://www.cve.org/CVERecord?id=CVE-2026-124915
    https://www.cve.org/CVERecord?id=CVE-2026-124917
    https://www.cve.org/CVERecord?id=CVE-2026-124918
    https://www.cve.org/CVERecord?id=CVE-2026-124919
    https://www.cve.org/CVERecord?id=CVE-2026-124922
    https://www.cve.org/CVERecord?id=CVE-2026-118021
    https://www.cve.org/CVERecord?id=CVE-2026-124924
    https://www.cve.org/CVERecord?id=CVE-2026-124926
    https://www.cve.org/CVERecord?id=CVE-2026-124927
    https://www.cve.org/CVERecord?id=CVE-2026-124929
    https://www.cve.org/CVERecord?id=CVE-2026-118024
    https://www.cve.org/CVERecord?id=CVE-2026-124930
    https://www.cve.org/CVERecord?id=CVE-2026-124931
    https://www.cve.org/CVERecord?id=CVE-2026-124932
    https://www.cve.org/CVERecord?id=CVE-2026-124933
    https://www.cve.org/CVERecord?id=CVE-2026-124934
    https://www.cve.org/CVERecord?id=CVE-2026-124935
    https://www.cve.org/CVERecord?id=CVE-2026-124938
    https://www.cve.org/CVERecord?id=CVE-2026-124939
    https://www.cve.org/CVERecord?id=CVE-2026-124940
    https://www.cve.org/CVERecord?id=CVE-2026-124941
    https://www.cve.org/CVERecord?id=CVE-2026-124942
    https://www.cve.org/CVERecord?id=CVE-2026-124948
    https://www.cve.org/CVERecord?id=CVE-2026-124951
  (* Security fix *)
xap/mozilla-thunderbird-153.7.0esr-x86_64-1.txz:  Upgraded.
  This update contains security fixes and improvements.
  For more information, see:
    https://www.mozilla.org/en-US/thunderbird/153.7.0esr/releasenotes/
    https://www.mozilla.org/en-US/security/advisories/mfsa2026-129/
    https://www.cve.org/CVERecord?id=CVE-2026-126132
    https://www.cve.org/CVERecord?id=CVE-2026-126133
    https://www.cve.org/CVERecord?id=CVE-2026-126134
    https://www.cve.org/CVERecord?id=CVE-2026-126135
    https://www.cve.org/CVERecord?id=CVE-2026-126136
    https://www.cve.org/CVERecord?id=CVE-2026-124853
    https://www.cve.org/CVERecord?id=CVE-2026-124854
    https://www.cve.org/CVERecord?id=CVE-2026-124855
    https://www.cve.org/CVERecord?id=CVE-2026-124856
    https://www.cve.org/CVERecord?id=CVE-2026-124857
    https://www.cve.org/CVERecord?id=CVE-2026-124858
    https://www.cve.org/CVERecord?id=CVE-2026-124859
    https://www.cve.org/CVERecord?id=CVE-2026-124860
    https://www.cve.org/CVERecord?id=CVE-2026-124861
    https://www.cve.org/CVERecord?id=CVE-2026-124862
    https://www.cve.org/CVERecord?id=CVE-2026-118007
    https://www.cve.org/CVERecord?id=CVE-2026-124863
    https://www.cve.org/CVERecord?id=CVE-2026-124864
    https://www.cve.org/CVERecord?id=CVE-2026-124865
    https://www.cve.org/CVERecord?id=CVE-2026-124866
    https://www.cve.org/CVERecord?id=CVE-2026-124868
    https://www.cve.org/CVERecord?id=CVE-2026-124869
    https://www.cve.org/CVERecord?id=CVE-2026-124870
    https://www.cve.org/CVERecord?id=CVE-2026-124872
    https://www.cve.org/CVERecord?id=CVE-2026-124873
    https://www.cve.org/CVERecord?id=CVE-2026-124874
    https://www.cve.org/CVERecord?id=CVE-2026-124875
    https://www.cve.org/CVERecord?id=CVE-2026-124876
    https://www.cve.org/CVERecord?id=CVE-2026-124877
    https://www.cve.org/CVERecord?id=CVE-2026-124879
    https://www.cve.org/CVERecord?id=CVE-2026-124880
    https://www.cve.org/CVERecord?id=CVE-2026-124881
    https://www.cve.org/CVERecord?id=CVE-2026-124882
    https://www.cve.org/CVERecord?id=CVE-2026-124883
    https://www.cve.org/CVERecord?id=CVE-2026-124884
    https://www.cve.org/CVERecord?id=CVE-2026-124885
    https://www.cve.org/CVERecord?id=CVE-2026-124886
    https://www.cve.org/CVERecord?id=CVE-2026-124887
    https://www.cve.org/CVERecord?id=CVE-2026-124888
    https://www.cve.org/CVERecord?id=CVE-2026-124889
    https://www.cve.org/CVERecord?id=CVE-2026-124890
    https://www.cve.org/CVERecord?id=CVE-2026-124891
    https://www.cve.org/CVERecord?id=CVE-2026-124892
    https://www.cve.org/CVERecord?id=CVE-2026-124893
    https://www.cve.org/CVERecord?id=CVE-2026-124894
    https://www.cve.org/CVERecord?id=CVE-2026-124895
    https://www.cve.org/CVERecord?id=CVE-2026-124896
    https://www.cve.org/CVERecord?id=CVE-2026-124897
    https://www.cve.org/CVERecord?id=CVE-2026-124898
    https://www.cve.org/CVERecord?id=CVE-2026-124899
    https://www.cve.org/CVERecord?id=CVE-2026-124901
    https://www.cve.org/CVERecord?id=CVE-2026-124902
    https://www.cve.org/CVERecord?id=CVE-2026-124903
    https://www.cve.org/CVERecord?id=CVE-2026-124905
    https://www.cve.org/CVERecord?id=CVE-2026-124906
    https://www.cve.org/CVERecord?id=CVE-2026-124907
    https://www.cve.org/CVERecord?id=CVE-2026-124909
    https://www.cve.org/CVERecord?id=CVE-2026-124910
    https://www.cve.org/CVERecord?id=CVE-2026-124912
    https://www.cve.org/CVERecord?id=CVE-2026-118019
    https://www.cve.org/CVERecord?id=CVE-2026-124913
    https://www.cve.org/CVERecord?id=CVE-2026-124914
    https://www.cve.org/CVERecord?id=CVE-2026-124915
    https://www.cve.org/CVERecord?id=CVE-2026-124917
    https://www.cve.org/CVERecord?id=CVE-2026-124918
    https://www.cve.org/CVERecord?id=CVE-2026-124919
    https://www.cve.org/CVERecord?id=CVE-2026-124922
    https://www.cve.org/CVERecord?id=CVE-2026-118021
    https://www.cve.org/CVERecord?id=CVE-2026-124924
    https://www.cve.org/CVERecord?id=CVE-2026-124926
    https://www.cve.org/CVERecord?id=CVE-2026-124927
    https://www.cve.org/CVERecord?id=CVE-2026-124929
    https://www.cve.org/CVERecord?id=CVE-2026-118024
    https://www.cve.org/CVERecord?id=CVE-2026-124930
    https://www.cve.org/CVERecord?id=CVE-2026-124931
    https://www.cve.org/CVERecord?id=CVE-2026-124932
    https://www.cve.org/CVERecord?id=CVE-2026-124933
    https://www.cve.org/CVERecord?id=CVE-2026-124934
    https://www.cve.org/CVERecord?id=CVE-2026-124935
    https://www.cve.org/CVERecord?id=CVE-2026-124938
    https://www.cve.org/CVERecord?id=CVE-2026-124939
    https://www.cve.org/CVERecord?id=CVE-2026-124940
    https://www.cve.org/CVERecord?id=CVE-2026-124941
    https://www.cve.org/CVERecord?id=CVE-2026-124942
    https://www.cve.org/CVERecord?id=CVE-2026-124948
    https://www.cve.org/CVERecord?id=CVE-2026-124951
  (* Security fix *)
xap/rxvt-unicode-9.32-x86_64-1.txz:  Upgraded.
isolinux/initrd.img:  Rebuilt.
kernels/*:  Upgraded.
usb-and-pxe-installers/usbboot.img:  Rebuilt.

a/inotify-tools-4.26.275-x86_64-1.txz:  Upgraded.
d/ccache-4.14.3-x86_64-1.txz:  Upgraded.
  This is a bugfix release.
  For more information, see:
    https://ccache.dev/releasenotes.html#_ccache_4_14_3
l/desktop-file-utils-0.29-x86_64-1.txz:  Upgraded.
l/graphviz-16.1.1-x86_64-1.txz:  Upgraded.
n/krb5-1.22.3-x86_64-1.txz:  Upgraded.
  This update fixes bugs and security issues.
  For more information, see:
    https://www.cve.org/CVERecord?id=CVE-2026-111423
    https://www.cve.org/CVERecord?id=CVE-2026-71199
    https://www.cve.org/CVERecord?id=CVE-2026-107884
    https://www.cve.org/CVERecord?id=CVE-2026-118380
    https://www.cve.org/CVERecord?id=CVE-2026-112322
    https://www.cve.org/CVERecord?id=CVE-2026-112323
    https://www.cve.org/CVERecord?id=CVE-2026-40355
    https://www.cve.org/CVERecord?id=CVE-2026-40356
    https://www.cve.org/CVERecord?id=CVE-2026-71200
    https://www.cve.org/CVERecord?id=CVE-2026-107364
    https://www.cve.org/CVERecord?id=CVE-2026-107708
    https://www.cve.org/CVERecord?id=CVE-2026-107778
    https://www.cve.org/CVERecord?id=CVE-2026-112314
    https://www.cve.org/CVERecord?id=CVE-2026-112315
    https://www.cve.org/CVERecord?id=CVE-2026-112316
    https://www.cve.org/CVERecord?id=CVE-2026-112317
    https://www.cve.org/CVERecord?id=CVE-2026-112318
    https://www.cve.org/CVERecord?id=CVE-2026-112319
    https://www.cve.org/CVERecord?id=CVE-2026-112320
    https://www.cve.org/CVERecord?id=CVE-2026-112321
    https://www.cve.org/CVERecord?id=CVE-2026-112323
    https://www.cve.org/CVERecord?id=CVE-2026-119079
  (* Security fix *)

ChangeLog Slackware arm 64 current

ChangeLog arm 64 Rss

a/libblockdev-3.6.0-aarch64-1.txz:  Upgraded.
a/usb_modeswitch-2.6.3-aarch64-1.txz:  Upgraded.
d/autoconf-archive-2026.11.11-aarch64-1.txz:  Upgraded.
d/dkms-3.4.5-aarch64-1.txz:  Upgraded.
d/flex-2.6.9-aarch64-1.txz:  Upgraded.
d/git-2.56.1-aarch64-1.txz:  Upgraded.
  This update fixes security issues.
  For more information, see:
    https://gitlab.com/git-scm/git/-/blob/HEAD/Documentation/RelNotes/2.56.1.adoc
    https://gitlab.com/git-scm/git/-/blob/HEAD/Documentation/RelNotes/2.50.2.adoc
    https://www.cve.org/CVERecord?id=CVE-2026-111760
    https://www.cve.org/CVERecord?id=CVE-2026-113408
    https://www.cve.org/CVERecord?id=CVE-2026-114466
    https://www.cve.org/CVERecord?id=CVE-2026-114467
    https://www.cve.org/CVERecord?id=CVE-2026-114469
    https://www.cve.org/CVERecord?id=CVE-2026-105437
  (* Security fix *)
kde/digikam-9.1.0-aarch64-6.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
kde/kimageformats-6.31.0-aarch64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
kde/kimageformats5-5.116.0-aarch64-8.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
kde/krita-6.0.4.1-aarch64-3.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/appstream-1.2.3-aarch64-1.txz:  Upgraded.
l/avahi-0.9_rc5-aarch64-1.txz:  Upgraded.
l/ffmpeg-9.0.2-aarch64-3.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/imagemagick-7.1.2_35-aarch64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/libjxl-0.13.0-aarch64-1.txz:  Upgraded.
  Shared library .so-version bump.
l/libtatsu-1.1.1-aarch64-1.txz:  Upgraded.
l/libvips-8.18.7-aarch64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
l/qtkeychain-0.18.0-aarch64-1.txz:  Upgraded.
l/sip-6.17.3-aarch64-1.txz:  Upgraded.
n/autofs-5.2.0-aarch64-1.txz:  Upgraded.
n/httpd-2.4.71-aarch64-1.txz:  Upgraded.
  This update fixes bugs and security issues:
  Heap corruption and RCE in assign_headers.
  mod_vhost_alias 1 byte stack buffer overwrite.
  mod_md NULL pointer dereference leads to child process crash.
  For more information, see:
    https://downloads.apache.org/httpd/CHANGES_2.4.71
    https://www.cve.org/CVERecord?id=CVE-2026-119618
    https://www.cve.org/CVERecord?id=CVE-2026-109163
    https://www.cve.org/CVERecord?id=CVE-2026-106023
  (* Security fix *)
n/mobile-broadband-provider-info-20261111-noarch-1.txz:  Upgraded.
n/sshfs-3.7.7-aarch64-1.txz:  Upgraded.
x/ibus-table-1.19.0-aarch64-1.txz:  Upgraded.
x/mesa-26.2.7-aarch64-1.txz:  Upgraded.
xap/freerdp-3.33.1-aarch64-1.txz:  Upgraded.
  This update fixes security issues.
  For more information, see:
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-x863-43r4-f7c2
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-m33m-4qxh-hq76
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-52rf-pppx-qm55
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-3664-pr8r-3254
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-rp99-f9qv-c446
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-23fv-6wrf-5hfq
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-f6v9-vx5q-vjpf
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-m6hp-4798-x78x
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-9c9j-2r7q-5gx2
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-ch3p-5r9r-w86p
    https://github.com/FreeRDP/FreeRDP/security/advisories/GHSA-76c4-7552-ffhv
  (* Security fix *)
xap/geeqie-3.4-aarch64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
xap/gimp-3.2.8-aarch64-2.txz:  Rebuilt.
  Recompiled against libjxl-0.13.0.
extra/tigervnc/tigervnc-1.16.2-aarch64-8.txz:  Rebuilt.
  Recompiled against xorg-server-21.1.26 to fix these security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  XRes QueryClientIds Request Size Overflow.
  XRes QueryResourceBytes Swap Path Size Overflow.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109904
    https://www.cve.org/CVERecord?id=CVE-2026-109094
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)

a/hwm-bw-raspberrypi-2026.11.10-aarch64-1.txz:  Upgraded.
  Upgraded to RPi boot firmware version..: 2026.11.09
  Upgraded to RPi EEPROM firmware version: 2026.11.10

  To update the firmware on your RPi's EEPROM, as root:

  $ rpi-eeprom-update -d

  This will report if there's newer firmware available.

  To update the firmware:
  $ rpi-eeprom-update -da

  If the firmware was successfully updated, power off:
  $ poweroff

  The boot loader will be upgraded once the machine is powered on again.

a/exfatprogs-1.4.4-aarch64-1.txz:  Upgraded.
a/kernel-firmware-20261109_69e51bb-noarch-1.txz:  Upgraded.
a/kernel_armv8-7.3.4-aarch64-1.txz:  Upgraded.
a/kmscon-10.1.1-aarch64-2.txz:  Rebuilt.
  kmscon.conf: set dpms-timeout=3600 to blank the screen after an hour instead
  of the default ten minutes.
a/sysvinit-scripts-16.0-noarch-11.txz:  Rebuilt.
  rc.modules: support loading modules from modules-load.d/ files, such as the
  one shipped in the ddcutil package.
  Thanks to gcosbug and ZhaoLin1457.
d/automake-1.20-noarch-1.txz:  Upgraded.
d/flex-2.6.5-aarch64-1.txz:  Upgraded.
d/kernel-headers-7.3.4-aarch64-1.txz:  Upgraded.
k/kernel-source-7.3.4-aarch64-1.txz:  Upgraded.
kde/stellarsolver-2.9-aarch64-1.txz:  Upgraded.
l/libgnt-2.15.0-aarch64-1.txz:  Upgraded.
l/libodfgen-0.1.9-aarch64-1.txz:  Upgraded.
l/libxmlb-0.3.30-aarch64-1.txz:  Upgraded.
l/lz4-1.11.1-aarch64-1.txz:  Upgraded.
x/xf86-video-fbdev-0.5.1-aarch64-6.txz:  Rebuilt.
x/xorg-server-21.1.26-aarch64-1.txz:  Upgraded.
  This update fixes security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  XRes QueryClientIds Request Size Overflow.
  XRes QueryResourceBytes Swap Path Size Overflow.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109904
    https://www.cve.org/CVERecord?id=CVE-2026-109094
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
x/xorg-server-xephyr-21.1.26-aarch64-1.txz:  Upgraded.
x/xorg-server-xnest-21.1.26-aarch64-1.txz:  Upgraded.
x/xorg-server-xvfb-21.1.26-aarch64-1.txz:  Upgraded.
x/xorg-server-xwayland-24.1.15-aarch64-1.txz:  Upgraded.
  This update fixes security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  XRes QueryClientIds Request Size Overflow.
  XRes QueryResourceBytes Swap Path Size Overflow.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109904
    https://www.cve.org/CVERecord?id=CVE-2026-109094
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
xap/mozilla-firefox-153.7.0esr-aarch64-1.txz:  Upgraded.
  This update contains security fixes and improvements.
  For more information, see:
    https://www.mozilla.org/en-US/firefox/153.7.0/releasenotes/
    https://www.mozilla.org/security/advisories/mfsa2026-127
    https://www.cve.org/CVERecord?id=CVE-2026-124853
    https://www.cve.org/CVERecord?id=CVE-2026-124854
    https://www.cve.org/CVERecord?id=CVE-2026-124855
    https://www.cve.org/CVERecord?id=CVE-2026-124856
    https://www.cve.org/CVERecord?id=CVE-2026-124857
    https://www.cve.org/CVERecord?id=CVE-2026-124858
    https://www.cve.org/CVERecord?id=CVE-2026-124859
    https://www.cve.org/CVERecord?id=CVE-2026-124860
    https://www.cve.org/CVERecord?id=CVE-2026-124861
    https://www.cve.org/CVERecord?id=CVE-2026-124862
    https://www.cve.org/CVERecord?id=CVE-2026-118007
    https://www.cve.org/CVERecord?id=CVE-2026-124863
    https://www.cve.org/CVERecord?id=CVE-2026-124864
    https://www.cve.org/CVERecord?id=CVE-2026-124865
    https://www.cve.org/CVERecord?id=CVE-2026-124866
    https://www.cve.org/CVERecord?id=CVE-2026-124868
    https://www.cve.org/CVERecord?id=CVE-2026-124869
    https://www.cve.org/CVERecord?id=CVE-2026-124870
    https://www.cve.org/CVERecord?id=CVE-2026-124872
    https://www.cve.org/CVERecord?id=CVE-2026-124873
    https://www.cve.org/CVERecord?id=CVE-2026-124874
    https://www.cve.org/CVERecord?id=CVE-2026-124875
    https://www.cve.org/CVERecord?id=CVE-2026-124876
    https://www.cve.org/CVERecord?id=CVE-2026-124877
    https://www.cve.org/CVERecord?id=CVE-2026-124879
    https://www.cve.org/CVERecord?id=CVE-2026-124880
    https://www.cve.org/CVERecord?id=CVE-2026-124881
    https://www.cve.org/CVERecord?id=CVE-2026-124882
    https://www.cve.org/CVERecord?id=CVE-2026-124883
    https://www.cve.org/CVERecord?id=CVE-2026-124884
    https://www.cve.org/CVERecord?id=CVE-2026-124885
    https://www.cve.org/CVERecord?id=CVE-2026-124886
    https://www.cve.org/CVERecord?id=CVE-2026-124887
    https://www.cve.org/CVERecord?id=CVE-2026-124888
    https://www.cve.org/CVERecord?id=CVE-2026-124889
    https://www.cve.org/CVERecord?id=CVE-2026-124890
    https://www.cve.org/CVERecord?id=CVE-2026-124891
    https://www.cve.org/CVERecord?id=CVE-2026-124892
    https://www.cve.org/CVERecord?id=CVE-2026-124893
    https://www.cve.org/CVERecord?id=CVE-2026-124894
    https://www.cve.org/CVERecord?id=CVE-2026-124895
    https://www.cve.org/CVERecord?id=CVE-2026-124896
    https://www.cve.org/CVERecord?id=CVE-2026-124897
    https://www.cve.org/CVERecord?id=CVE-2026-124898
    https://www.cve.org/CVERecord?id=CVE-2026-124899
    https://www.cve.org/CVERecord?id=CVE-2026-124901
    https://www.cve.org/CVERecord?id=CVE-2026-124902
    https://www.cve.org/CVERecord?id=CVE-2026-124903
    https://www.cve.org/CVERecord?id=CVE-2026-124905
    https://www.cve.org/CVERecord?id=CVE-2026-124906
    https://www.cve.org/CVERecord?id=CVE-2026-124907
    https://www.cve.org/CVERecord?id=CVE-2026-124909
    https://www.cve.org/CVERecord?id=CVE-2026-124910
    https://www.cve.org/CVERecord?id=CVE-2026-124912
    https://www.cve.org/CVERecord?id=CVE-2026-118019
    https://www.cve.org/CVERecord?id=CVE-2026-124913
    https://www.cve.org/CVERecord?id=CVE-2026-124914
    https://www.cve.org/CVERecord?id=CVE-2026-124915
    https://www.cve.org/CVERecord?id=CVE-2026-124917
    https://www.cve.org/CVERecord?id=CVE-2026-124918
    https://www.cve.org/CVERecord?id=CVE-2026-124919
    https://www.cve.org/CVERecord?id=CVE-2026-124922
    https://www.cve.org/CVERecord?id=CVE-2026-118021
    https://www.cve.org/CVERecord?id=CVE-2026-124924
    https://www.cve.org/CVERecord?id=CVE-2026-124926
    https://www.cve.org/CVERecord?id=CVE-2026-124927
    https://www.cve.org/CVERecord?id=CVE-2026-124929
    https://www.cve.org/CVERecord?id=CVE-2026-118024
    https://www.cve.org/CVERecord?id=CVE-2026-124930
    https://www.cve.org/CVERecord?id=CVE-2026-124931
    https://www.cve.org/CVERecord?id=CVE-2026-124932
    https://www.cve.org/CVERecord?id=CVE-2026-124933
    https://www.cve.org/CVERecord?id=CVE-2026-124934
    https://www.cve.org/CVERecord?id=CVE-2026-124935
    https://www.cve.org/CVERecord?id=CVE-2026-124938
    https://www.cve.org/CVERecord?id=CVE-2026-124939
    https://www.cve.org/CVERecord?id=CVE-2026-124940
    https://www.cve.org/CVERecord?id=CVE-2026-124941
    https://www.cve.org/CVERecord?id=CVE-2026-124942
    https://www.cve.org/CVERecord?id=CVE-2026-124948
    https://www.cve.org/CVERecord?id=CVE-2026-124951
  (* Security fix *)
xap/mozilla-thunderbird-153.7.0esr-aarch64-1.txz:  Upgraded.
  This update contains security fixes and improvements.
  For more information, see:
    https://www.mozilla.org/en-US/thunderbird/153.7.0esr/releasenotes/
    https://www.mozilla.org/en-US/security/advisories/mfsa2026-129/
    https://www.cve.org/CVERecord?id=CVE-2026-126132
    https://www.cve.org/CVERecord?id=CVE-2026-126133
    https://www.cve.org/CVERecord?id=CVE-2026-126134
    https://www.cve.org/CVERecord?id=CVE-2026-126135
    https://www.cve.org/CVERecord?id=CVE-2026-126136
    https://www.cve.org/CVERecord?id=CVE-2026-124853
    https://www.cve.org/CVERecord?id=CVE-2026-124854
    https://www.cve.org/CVERecord?id=CVE-2026-124855
    https://www.cve.org/CVERecord?id=CVE-2026-124856
    https://www.cve.org/CVERecord?id=CVE-2026-124857
    https://www.cve.org/CVERecord?id=CVE-2026-124858
    https://www.cve.org/CVERecord?id=CVE-2026-124859
    https://www.cve.org/CVERecord?id=CVE-2026-124860
    https://www.cve.org/CVERecord?id=CVE-2026-124861
    https://www.cve.org/CVERecord?id=CVE-2026-124862
    https://www.cve.org/CVERecord?id=CVE-2026-118007
    https://www.cve.org/CVERecord?id=CVE-2026-124863
    https://www.cve.org/CVERecord?id=CVE-2026-124864
    https://www.cve.org/CVERecord?id=CVE-2026-124865
    https://www.cve.org/CVERecord?id=CVE-2026-124866
    https://www.cve.org/CVERecord?id=CVE-2026-124868
    https://www.cve.org/CVERecord?id=CVE-2026-124869
    https://www.cve.org/CVERecord?id=CVE-2026-124870
    https://www.cve.org/CVERecord?id=CVE-2026-124872
    https://www.cve.org/CVERecord?id=CVE-2026-124873
    https://www.cve.org/CVERecord?id=CVE-2026-124874
    https://www.cve.org/CVERecord?id=CVE-2026-124875
    https://www.cve.org/CVERecord?id=CVE-2026-124876
    https://www.cve.org/CVERecord?id=CVE-2026-124877
    https://www.cve.org/CVERecord?id=CVE-2026-124879
    https://www.cve.org/CVERecord?id=CVE-2026-124880
    https://www.cve.org/CVERecord?id=CVE-2026-124881
    https://www.cve.org/CVERecord?id=CVE-2026-124882
    https://www.cve.org/CVERecord?id=CVE-2026-124883
    https://www.cve.org/CVERecord?id=CVE-2026-124884
    https://www.cve.org/CVERecord?id=CVE-2026-124885
    https://www.cve.org/CVERecord?id=CVE-2026-124886
    https://www.cve.org/CVERecord?id=CVE-2026-124887
    https://www.cve.org/CVERecord?id=CVE-2026-124888
    https://www.cve.org/CVERecord?id=CVE-2026-124889
    https://www.cve.org/CVERecord?id=CVE-2026-124890
    https://www.cve.org/CVERecord?id=CVE-2026-124891
    https://www.cve.org/CVERecord?id=CVE-2026-124892
    https://www.cve.org/CVERecord?id=CVE-2026-124893
    https://www.cve.org/CVERecord?id=CVE-2026-124894
    https://www.cve.org/CVERecord?id=CVE-2026-124895
    https://www.cve.org/CVERecord?id=CVE-2026-124896
    https://www.cve.org/CVERecord?id=CVE-2026-124897
    https://www.cve.org/CVERecord?id=CVE-2026-124898
    https://www.cve.org/CVERecord?id=CVE-2026-124899
    https://www.cve.org/CVERecord?id=CVE-2026-124901
    https://www.cve.org/CVERecord?id=CVE-2026-124902
    https://www.cve.org/CVERecord?id=CVE-2026-124903
    https://www.cve.org/CVERecord?id=CVE-2026-124905
    https://www.cve.org/CVERecord?id=CVE-2026-124906
    https://www.cve.org/CVERecord?id=CVE-2026-124907
    https://www.cve.org/CVERecord?id=CVE-2026-124909
    https://www.cve.org/CVERecord?id=CVE-2026-124910
    https://www.cve.org/CVERecord?id=CVE-2026-124912
    https://www.cve.org/CVERecord?id=CVE-2026-118019
    https://www.cve.org/CVERecord?id=CVE-2026-124913
    https://www.cve.org/CVERecord?id=CVE-2026-124914
    https://www.cve.org/CVERecord?id=CVE-2026-124915
    https://www.cve.org/CVERecord?id=CVE-2026-124917
    https://www.cve.org/CVERecord?id=CVE-2026-124918
    https://www.cve.org/CVERecord?id=CVE-2026-124919
    https://www.cve.org/CVERecord?id=CVE-2026-124922
    https://www.cve.org/CVERecord?id=CVE-2026-118021
    https://www.cve.org/CVERecord?id=CVE-2026-124924
    https://www.cve.org/CVERecord?id=CVE-2026-124926
    https://www.cve.org/CVERecord?id=CVE-2026-124927
    https://www.cve.org/CVERecord?id=CVE-2026-124929
    https://www.cve.org/CVERecord?id=CVE-2026-118024
    https://www.cve.org/CVERecord?id=CVE-2026-124930
    https://www.cve.org/CVERecord?id=CVE-2026-124931
    https://www.cve.org/CVERecord?id=CVE-2026-124932
    https://www.cve.org/CVERecord?id=CVE-2026-124933
    https://www.cve.org/CVERecord?id=CVE-2026-124934
    https://www.cve.org/CVERecord?id=CVE-2026-124935
    https://www.cve.org/CVERecord?id=CVE-2026-124938
    https://www.cve.org/CVERecord?id=CVE-2026-124939
    https://www.cve.org/CVERecord?id=CVE-2026-124940
    https://www.cve.org/CVERecord?id=CVE-2026-124941
    https://www.cve.org/CVERecord?id=CVE-2026-124942
    https://www.cve.org/CVERecord?id=CVE-2026-124948
    https://www.cve.org/CVERecord?id=CVE-2026-124951
  (* Security fix *)
xap/rxvt-unicode-9.32-aarch64-1.txz:  Upgraded.
installer/*:  Rebuilt.
kernels/*:  Upgraded.

ChangeLog Slackware stable

ChangeLog x86 Rss - ChangeLog x86_64 Rss

extra/tigervnc/tigervnc-1.16.2-x86_64-5_slack15.0.txz:  Rebuilt.
  Recompiled against xorg-server-1.20.14, including patches for
  security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
patches/packages/git-2.50.2-x86_64-1_slack15.0.txz:  Upgraded.
  It's probably time to bump this to a version that has security support.
  This update fixes security issues.
  For more information, see:
    https://gitlab.com/git-scm/git/-/blob/HEAD/Documentation/RelNotes/2.50.2.adoc
    https://www.cve.org/CVERecord?id=CVE-2026-111760
    https://www.cve.org/CVERecord?id=CVE-2026-113408
    https://www.cve.org/CVERecord?id=CVE-2026-114466
    https://www.cve.org/CVERecord?id=CVE-2026-114467
    https://www.cve.org/CVERecord?id=CVE-2026-114469
    https://www.cve.org/CVERecord?id=CVE-2026-105437
  (* Security fix *)
patches/packages/httpd-2.4.71-x86_64-1_slack15.0.txz:  Upgraded.
  This update fixes bugs and security issues:
  Heap corruption and RCE in assign_headers.
  mod_vhost_alias 1 byte stack buffer overwrite.
  mod_md NULL pointer dereference leads to child process crash.
  For more information, see:
    https://downloads.apache.org/httpd/CHANGES_2.4.71
    https://www.cve.org/CVERecord?id=CVE-2026-119618
    https://www.cve.org/CVERecord?id=CVE-2026-109163
    https://www.cve.org/CVERecord?id=CVE-2026-106023
  (* Security fix *)

patches/packages/xorg-server-1.20.14-x86_64-23_slack15.0.txz:  Rebuilt.
  This update fixes security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
patches/packages/xorg-server-xephyr-1.20.14-x86_64-23_slack15.0.txz:  Rebuilt.
patches/packages/xorg-server-xnest-1.20.14-x86_64-23_slack15.0.txz:  Rebuilt.
patches/packages/xorg-server-xvfb-1.20.14-x86_64-23_slack15.0.txz:  Rebuilt.
patches/packages/xorg-server-xwayland-21.1.4-x86_64-21_slack15.0.txz:  Rebuilt.
  This update fixes security issues:
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)

patches/packages/krb5-1.22.3-x86_64-1_slack15.0.txz:  Upgraded.
  This update fixes bugs and security issues.
  For more information, see:
    https://www.cve.org/CVERecord?id=CVE-2026-111423
    https://www.cve.org/CVERecord?id=CVE-2026-71199
    https://www.cve.org/CVERecord?id=CVE-2026-107884
    https://www.cve.org/CVERecord?id=CVE-2026-118380
    https://www.cve.org/CVERecord?id=CVE-2026-112322
    https://www.cve.org/CVERecord?id=CVE-2026-112323
    https://www.cve.org/CVERecord?id=CVE-2026-40355
    https://www.cve.org/CVERecord?id=CVE-2026-40356
    https://www.cve.org/CVERecord?id=CVE-2026-71200
    https://www.cve.org/CVERecord?id=CVE-2026-107364
    https://www.cve.org/CVERecord?id=CVE-2026-107708
    https://www.cve.org/CVERecord?id=CVE-2026-107778
    https://www.cve.org/CVERecord?id=CVE-2026-112314
    https://www.cve.org/CVERecord?id=CVE-2026-112315
    https://www.cve.org/CVERecord?id=CVE-2026-112316
    https://www.cve.org/CVERecord?id=CVE-2026-112317
    https://www.cve.org/CVERecord?id=CVE-2026-112318
    https://www.cve.org/CVERecord?id=CVE-2026-112319
    https://www.cve.org/CVERecord?id=CVE-2026-112320
    https://www.cve.org/CVERecord?id=CVE-2026-112321
    https://www.cve.org/CVERecord?id=CVE-2026-112323
    https://www.cve.org/CVERecord?id=CVE-2026-119079
  (* Security fix *)

ChangeLog Slackware arm stable

ChangeLog arm Rss

extra/tigervnc/tigervnc-1.16.2-arm-5_slack15.0.txz:  Rebuilt.
  Recompiled against xorg-server-1.20.14, including patches for
  security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
patches/packages/git-2.50.2-arm-1_slack15.0.txz:  Upgraded.
  It's probably time to bump this to a version that has security support.
  This update fixes security issues.
  For more information, see:
    https://gitlab.com/git-scm/git/-/blob/HEAD/Documentation/RelNotes/2.50.2.adoc
    https://www.cve.org/CVERecord?id=CVE-2026-111760
    https://www.cve.org/CVERecord?id=CVE-2026-113408
    https://www.cve.org/CVERecord?id=CVE-2026-114466
    https://www.cve.org/CVERecord?id=CVE-2026-114467
    https://www.cve.org/CVERecord?id=CVE-2026-114469
    https://www.cve.org/CVERecord?id=CVE-2026-105437
  (* Security fix *)
patches/packages/httpd-2.4.71-arm-1_slack15.0.txz:  Upgraded.
  This update fixes bugs and security issues:
  Heap corruption and RCE in assign_headers.
  mod_vhost_alias 1 byte stack buffer overwrite.
  mod_md NULL pointer dereference leads to child process crash.
  For more information, see:
    https://downloads.apache.org/httpd/CHANGES_2.4.71
    https://www.cve.org/CVERecord?id=CVE-2026-119618
    https://www.cve.org/CVERecord?id=CVE-2026-109163
    https://www.cve.org/CVERecord?id=CVE-2026-106023
  (* Security fix *)

patches/packages/xorg-server-1.20.14-arm-23_slack15.0.txz:  Rebuilt.
  This update fixes security issues:
  EDID DS_RANGES Out-Of-Bounds Write.
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109091
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)
patches/packages/xorg-server-xephyr-1.20.14-arm-23_slack15.0.txz:  Rebuilt.
patches/packages/xorg-server-xnest-1.20.14-arm-23_slack15.0.txz:  Rebuilt.
patches/packages/xorg-server-xvfb-1.20.14-arm-23_slack15.0.txz:  Rebuilt.
patches/packages/xorg-server-xwayland-21.1.4-arm-15_slack15.0.txz:  Rebuilt.
  This update fixes security issues:
  XvShmPutImage Shared-Memory Bounds Overflow.
  XTestFakeInput Valuator Stack Out-Of-Bounds Write.
  glamor Xv Image Size Integer Overflow.
  XvPutImage Negative Image Size Length Bypass.
  XvQueryImageAttributes Negative Size Reply.
  For more information, see:
    https://lists.x.org/archives/xorg-announce/2026-November/003759.html
    https://www.cve.org/CVERecord?id=CVE-2026-109092
    https://www.cve.org/CVERecord?id=CVE-2026-109093
    https://www.cve.org/CVERecord?id=CVE-2026-109095
    https://www.cve.org/CVERecord?id=CVE-2026-109096
    https://www.cve.org/CVERecord?id=CVE-2026-109903
  (* Security fix *)

patches/packages/ca-certificates-20261107-noarch-1_slack15.0.txz:  Upgraded.
  This update provides the latest CA certificates to check for the
  authenticity of SSL connections.
patches/packages/krb5-1.22.3-arm-1_slack15.0.txz:  Upgraded.
  This update fixes bugs and security issues.
  For more information, see:
    https://www.cve.org/CVERecord?id=CVE-2026-111423
    https://www.cve.org/CVERecord?id=CVE-2026-71199
    https://www.cve.org/CVERecord?id=CVE-2026-107884
    https://www.cve.org/CVERecord?id=CVE-2026-118380
    https://www.cve.org/CVERecord?id=CVE-2026-112322
    https://www.cve.org/CVERecord?id=CVE-2026-112323
    https://www.cve.org/CVERecord?id=CVE-2026-40355
    https://www.cve.org/CVERecord?id=CVE-2026-40356
    https://www.cve.org/CVERecord?id=CVE-2026-71200
    https://www.cve.org/CVERecord?id=CVE-2026-107364
    https://www.cve.org/CVERecord?id=CVE-2026-107708
    https://www.cve.org/CVERecord?id=CVE-2026-107778
    https://www.cve.org/CVERecord?id=CVE-2026-112314
    https://www.cve.org/CVERecord?id=CVE-2026-112315
    https://www.cve.org/CVERecord?id=CVE-2026-112316
    https://www.cve.org/CVERecord?id=CVE-2026-112317
    https://www.cve.org/CVERecord?id=CVE-2026-112318
    https://www.cve.org/CVERecord?id=CVE-2026-112319
    https://www.cve.org/CVERecord?id=CVE-2026-112320
    https://www.cve.org/CVERecord?id=CVE-2026-112321
    https://www.cve.org/CVERecord?id=CVE-2026-112323
    https://www.cve.org/CVERecord?id=CVE-2026-119079
  (* Security fix *)

Aggiornamenti

Rss

Aggiornamenti di script e guide

24/02/2022: Aggiornato HowTo Automatizzare l'aggiornamento di Slackware
15/12/2015: Aggiornato HowTo automatizzare la compilazione del kernel
15/12/2015: Aggiornato HowTo Automatizzare l'aggiornamento di Slackware current
24/11/2015: Aggiornato HowTo automatizzare la compilazione del kernel
22/11/2015: Aggiornato HowTo Automatizzare l'aggiornamento di Slackware current
07/11/2015: Aggiornato HowTo automatizzare la compilazione del kernel
05/11/2015: Nuovo HowTo Automatizzare l'aggiornamento di Slackware current
30/10/2015: Aggiornato HowTo Automatizzare la prima configurazione di Slackware
26/05/2015: Aggiornato HowTo mini Slackware su pendrive
07/05/2015: Aggiornato HowTo automatizzare la compilazione del kernel
13/04/2015: Aggiornato HowTo automatizzare la compilazione del kernel
02/04/2015: Aggiornato HowTo automatizzare la compilazione del kernel


Script mini Slackware su pendrive

Vi presento uno script bash che crea una mini Slackware su pendrive in automatico. script
Questo esempio fa riferimento a Slackware 14.0 a 32bit ma può essere facilmente adattato a qualsiasi altra versione.
Cerca i pacchetti elencati nell'array se sono già presenti nella directory impostata, se non li trova e se c'è il dvd di Slackware montato li copia da esso, altrimenti li scarica da internet.
Leggi tutto...

Nuova sezione "App Android"

⇦ Ho aggiunto una nuova pagina a questo sito che raccoglie le mie app. info

Possono essere tutte scaricate dal Play Store di Google.

Script web radio italiane in bash

Un piccolo script in bash che sfrutta kdialog come semplice interfaccia. script

Nella sezione download è possibile scaricare anche il pacchetto di installazione per slackware.

Leggi tutto...

Viva lo spazio

info

Ho 100MiB in più e aggiungo qualcosa al repository ;-)


Traduzione di un pensiero di Dusty Wilson

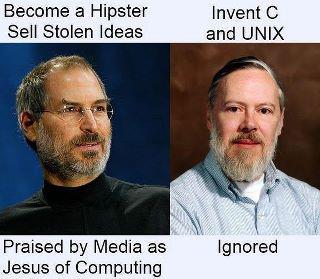
Ho trovato questo pensiero di Dusty Wilson in inglese su Google+ e lo riporto in parte qui tradotto perché secondo me il motivo di fondo che lo ha spinto a scrivere ciò, è quello che si vede nell'immagine ed è la stessa cosa che ho pensato io quando è morto Dennis Ritchie: Dennis Ritchie vs Steve Jobs

Dennis Ritchie ha co-inventato C che è la base di praticamente tutto ciò che riguarda i computer. Ha co-inventato UNIX che è alla base di tutto nei computer tranne che di Windows (anche se Windows è stato molto, molto molto influenzato da esso). Apple OS X è una piattaforma basata su UNIX. Ma molta gente pensa che Steve Jobs ha fatto tutto da solo e che dovrebbe essere lodato come un salvatore. Non solo ha preso "in prestito" idee, progetti e funzionalità da tutti gli altri, ha piagnucolato se qualcuno abbia mai fatto lo stesso. Nel 1996 ha detto: "Noi siamo sempre stati senza vergogna di rubare grandi idee." Nel 2005 ha detto: "Sono senza vergogna quelli che ci copiano". Quest'anno ha detto "Vado a distruggere Android, perché è un prodotto rubato. Sono disposto ad andare in questa guerra termonucleare" e poi, quasi subito dopo ha rilasciato iOS 5 con una tonnellata di caratteristiche già introdotte in Android. Il ragazzo è/era uno stronzo. Non ho pazienza per un ipocrita come lui.


Condividi sui tuoi social preferiti!

Telegram Facebook Linkedin Twitter Pinterest
.
↑